

We generate the proof
What Finite State carries
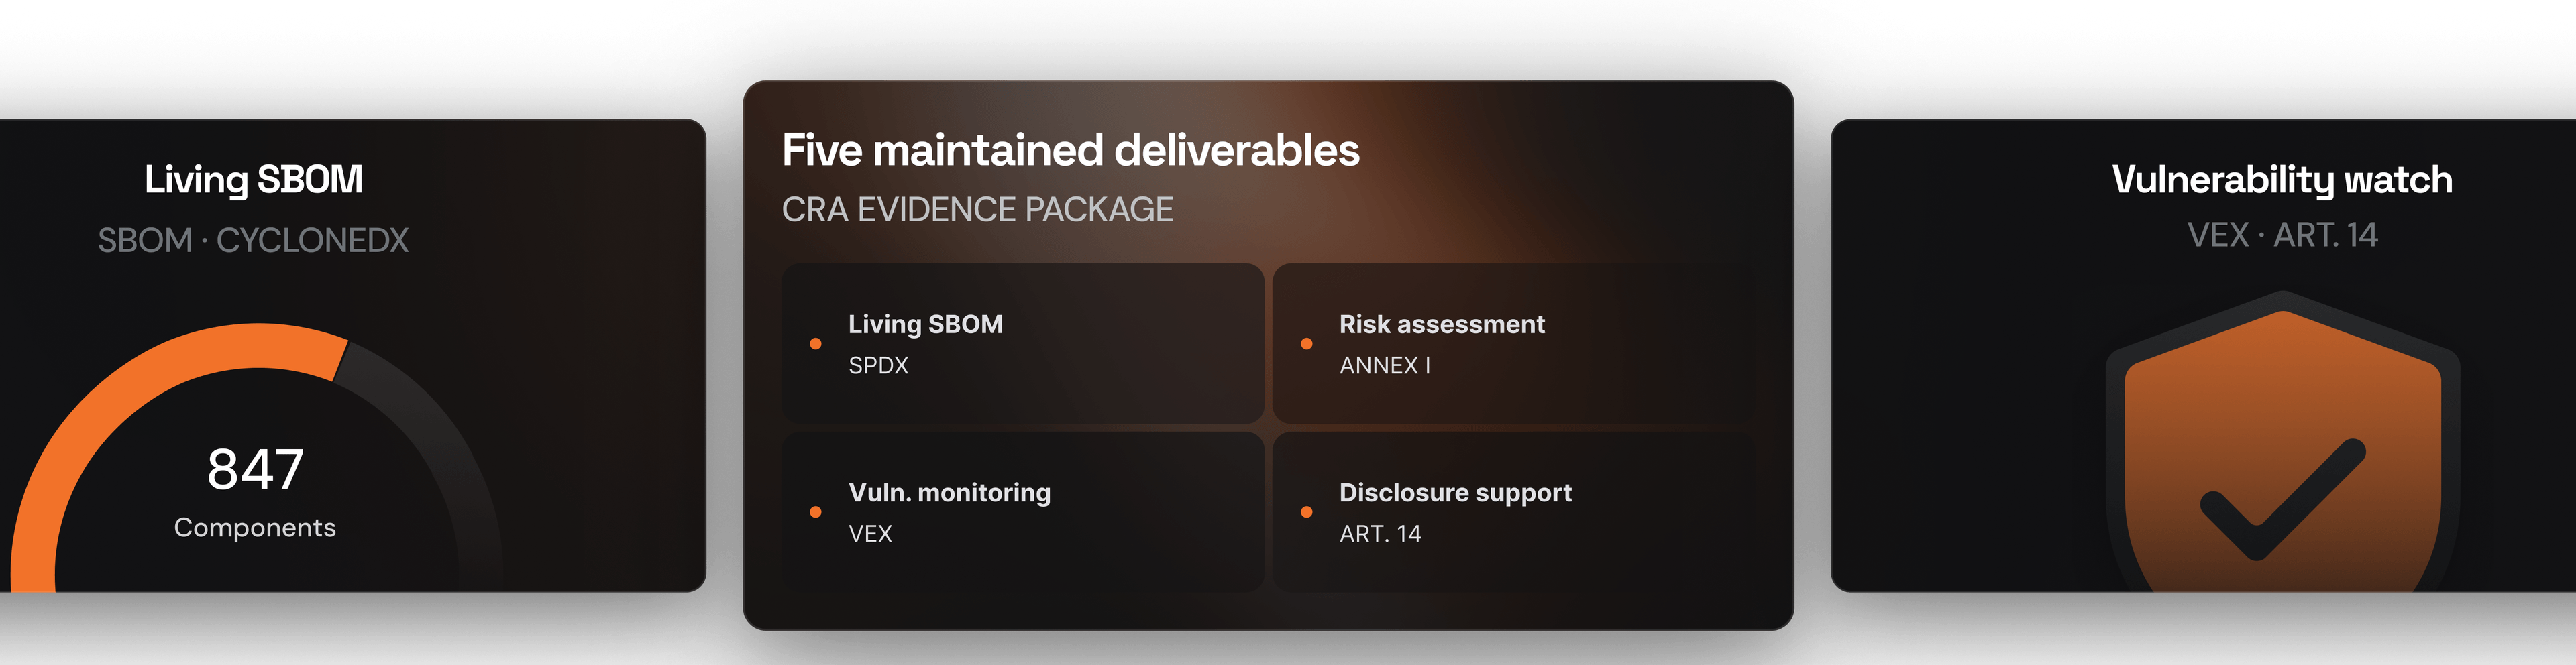
Generates SBOM & VEX from what you ship
Runs the cybersecurity risk assessment
Monitors vulnerabilities continuously
Drafts disclosures & your CVD policy
Assembles technical docs & the DoC template
The Cyber Resilience Act applies to any manufacturer placing products on the EU market, wherever the company is based. Finite State analyzes what actually shipped, maintains the evidence across every release, and assembles the technical file behind your Declaration.
How It Works
In March 2026, Quectel publicly stated its module portfolio supports CRA compliance ahead of the September deadline.

Nothing in the regulation tells you which requirements apply to your product, whether your existing scanner output counts as evidence, or what the technical file has to contain. Harmonised standards that would settle those questions have not been published yet. Meanwhile Article 14 reporting obligations started applying in September 2026, including to products already in the market.
The platform inventories every component in your binary, including supplier firmware that arrives with no manifest to read. Our team classifies the product, maps it against the essential requirements, names the gaps, and sequences them. For products already in market, we establish whether conformity is reachable through software updates or blocked by hardware.
A CVE list with no product context sends engineers after code paths that cannot be reached in your device. The platform ranks findings by reachability and exploitability. Our product security team turns that into a risk assessment an assessor can follow.
The platform checks new disclosures against your specific product and filters to weaponized vulnerabilities, giving your team a daily punch list. When something is actively exploited, our team drafts the notifications against the reporting clocks and coordinates with your PSIRT and communications teams.
Every deliverable is generated from the product you ship and maintained across releases. Each maps to a specific CRA obligation.
Ownership + Scope
We generate the proof
Generates SBOM & VEX from what you ship
Runs the cybersecurity risk assessment
Monitors vulnerabilities continuously
Drafts disclosures & your CVD policy
Assembles technical docs & the DoC template
You own the decision
Remediation & the Article 14 determination
ENISA / SRP filing
Signed Declaration of Conformity
Manufacturer accountability
Quectel Wireless Solutions has worked with Finite State since 2022, across a portfolio representing roughly 70% of North American IoT modules shipped in an 18-month window. In March 2026, Quectel publicly stated its module portfolio supports CRA compliance ahead of the September deadline. This is what four years of the work looks like, not what month one requires.
Average risk score vs. industry, 10 = best
Of US-shipped modules with those scores since 2022
Of all connected products Finite State analyzed
“We started this work before any regulator asked us to, and that head start is why we can answer CRA questions today with documentation rather than promises.”
“When an enterprise customer asks us for an SBOM or penetration testing data, we can produce it.”
Article 64 sets fines at up to 15 million euros or 2.5% of total worldwide annual turnover, whichever is higher. Market surveillance authorities can also require corrective action, restrict distribution, or order withdrawal. A product pulled from sale costs revenue on the day it happens.
Entered into force. The transition period starts.
Notified bodies can begin operating.
Article 14 reporting obligations apply. 24 hours for early warning, 72 for notification, 14 days for the final report. Applies to products already on the market.
Full application. Products without conformity cannot be placed on the EU market.
One product, one call. You leave knowing your class, your assessment route, and the deliverables that route requires. Map your product to the CRA.