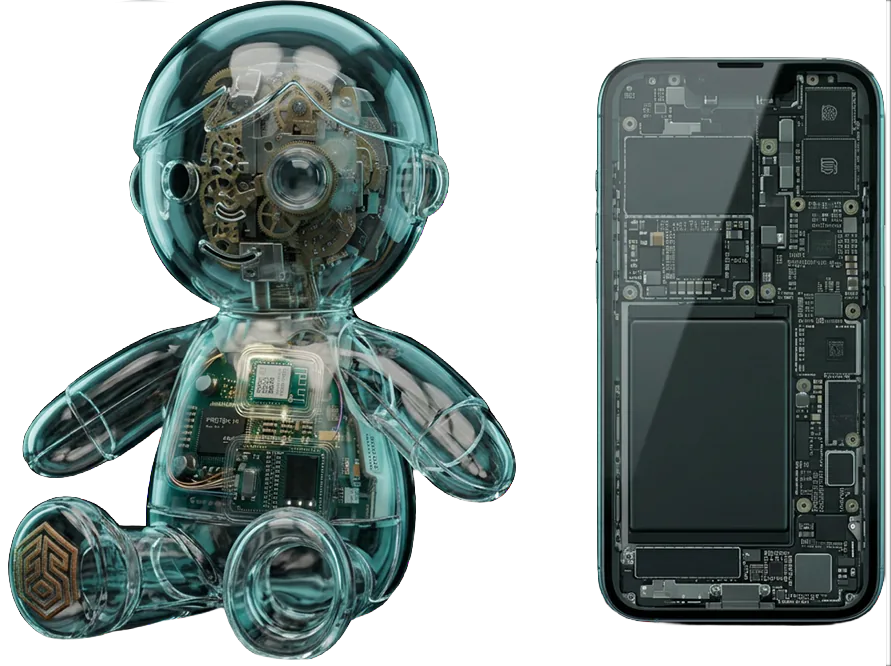
You can’t see inside it.
It’s compiled, stripped and assembled from dozens of suppliers. Your own code may be a small fraction of what ships, and the manufacturer answers for all of it.
What’s inside matters
Your firmware has to keep up with both. Finite State automates product security for connected devices: we read the compiled firmware you ship, attack every build before adversaries can, drive the fix for what’s real and keep the proof regulators ask for.
See what’s inside your firmwareIt’s compiled, stripped and assembled from dozens of suppliers. Your own code may be a small fraction of what ships, and the manufacturer answers for all of it.
A fix travels from chipset vendor to OEM to over-the-air update, with QA and recertification at every step. Attackers need hours.
CRA reporting runs on a 24-hour clock. FDA wants premarket evidence. The FCC wants to know what’s inside and who made it. Buyers send questionnaires.
There aren’t enough product security engineers in the world to do this by hand. So we automated it, and your team makes the calls.
No source code needed.
Finite State analyzes the build that actually ships: the compiled firmware itself, not the manifest or the source tree. We unpack it down to the file and map every component, including the ones suppliers never declared: software, hardware, architecture and who supplied it. It takes minutes, so you can check every release, every variant and every supplier image.
When a new flaw drops, we find every product that shares the vulnerable code, even before it has a CVE.
The Product Security Assurance platform for connected devices.






Manifests miss 1 in 6 components. Finite State builds a ground-truth software inventory by analyzing compiled binaries, source, and supplier code—revealing every hidden dependency in the build you ship.
AI made finding vulnerabilities cheap. Triage is where the time goes. Every finding gets four checks, automatically. Your engineers work the handful that pass; the rest close on their own, each with a VEX record that says why.
None of them in NVD.
Proving Ground attacks every build the way an adversary would: it unpacks the image, stands up its services, hunts for new flaws and chains them into exploits, with the newest techniques as they’re published. No source code required.
For less than one manual pen test per product, per year.
Every finding has to survive agents trying to disprove it. Proven issues come with a working proof of concept, and every fix is re-tested on the next build. Keep your experts for certification work, or replace the annual test.
Start with a Binary TeardownComing soon: the Beacon Project
Get notifiedReady before the regulator asks.
The CRA wants a report within 24 hours. The FDA wants evidence before you submit. The FCC wants to know who made every part. Finite State keeps one record for each product, with the SBOM and HBOM, every vulnerability decision and its reason, every Proving Ground result and the threat model, and generates each regulator’s report from it.
When an exploited flaw hits a component you ship, the CRA clock starts in the platform. Agents draft the 24-hour, 72-hour and 14-day reports, and your team reviews and signs them.
Exploited flaws reported within 24 hours; full security obligations from December 2027.
An SBOM and cybersecurity evidence in every premarket submission.
What’s inside and who made it, for certification and market access.
Lifecycle security and software update evidence per vehicle type.
Threat analysis, vulnerability analysis and cybersecurity testing.
Secure development and component security requirements.
Baseline security provisions for consumer devices.
Analysis, triage, testing and evidence run inside your CI and your tools. Your team makes every call.
Bring your own agents through our API and MCP server.
See the platformOur product security engineers tune the agents to your products, suppliers and regulations, then review what they draft with your team before you approve it.
See how we work togetherWe run your product security program, from PSIRT to CRA reporting and testing, with our agents doing the heavy lifting. You approve what goes out.
Scope your program“Using Finite State feels like showing up to a test with X-ray vision. Instead of wasting days on manual reverse engineering, I get an enriched SBOM, mapped vulnerabilities, crypto misuse, and even hard-coded secrets before I start. That context lets me focus on validating what’s truly exploitable—faster, deeper, and with better results.”
“Finite State fits seamlessly into our workflow. The reachability analysis and triage features make it easy to cut through the noise and focus on the vulnerabilities that actually matter.”
“I really value the live support. Having a chat feature staffed across time zones means whenever I need help, there’s someone knowledgeable ready to jump in.”
“The unified platform replaced four separate tools. Integration with our CI/CD pipeline was seamless, and we caught critical vulnerabilities before production.”
“Compliance reporting that used to take weeks now takes hours. The platform automatically maps our security posture to regulatory requirements.”
“With Finite State, we finally have continuous monitoring that makes risks and vulnerabilities visible. It’s transformed how quickly we can identify and address issues.”
“Finite State is a clear step above our previous SCA vendor. Continuous monitoring surfaces compliance & regulatory needs, while global search helped us uncover a major vulnerability we’d overlooked. With one centralized, multi-tenant platform, we can control access, streamline workflows, & give teams the visibility they need.”
“Reachability is the big topic in R&D right now. We won’t even consider tools that don’t have strong reachability assessments — and Finite State delivers!”
“Finite State fills a critical gap for us by analyzing mobile app binaries when source code isn’t available. It handles the wide variety of firmware formats we use and continuously monitors for new vulnerabilities, which gives us confidence nothing slips through the cracks.”
“Finite State’s feature set is a huge step forward for us. It’s a big improvement in how we approach product security and compliance.”
“Finite State has transformed how we approach firmware security. The automated SBOM generation and vulnerability detection gives us confidence in every release.”
“Before Finite State, we struggled to maintain visibility into our software supply chain. Now we have complete transparency and can respond to vulnerabilities in hours, not weeks.”
“UN R155 compliance requires demonstrable security processes. Finite State’s platform documents our entire vulnerability management lifecycle automatically.”
“Each vehicle has over 100 ECUs from dozens of suppliers. Finite State analyzes the entire supply chain, identifying risks before they reach production.”
“EV charging infrastructure is a critical attack surface. Finite State’s binary analysis found backdoors in third-party firmware we never would have caught.”
Every flaw in the firmware you’ve shipped is about to be found. Find it, prove it and fix it first.