Back to Webinars
Compliance & Regulations
Feb 19, 2026
Why Bottom-Up Vulnerability Management Breaks at Scale
Why Bottom-Up Vulnerability Management Breaks at Scale
So, you know, we've seen some smaller orgs actually very successfully do kind of the bottom up approach where you look at your third party library vulnerabilities.
You look at your supply chain dependencies. You can map them pretty easily. Maybe you only have fifteen developers and two products on the market, and then you can kind of use the outcomes of that to figure out who you have to satisfy at the auditor level.
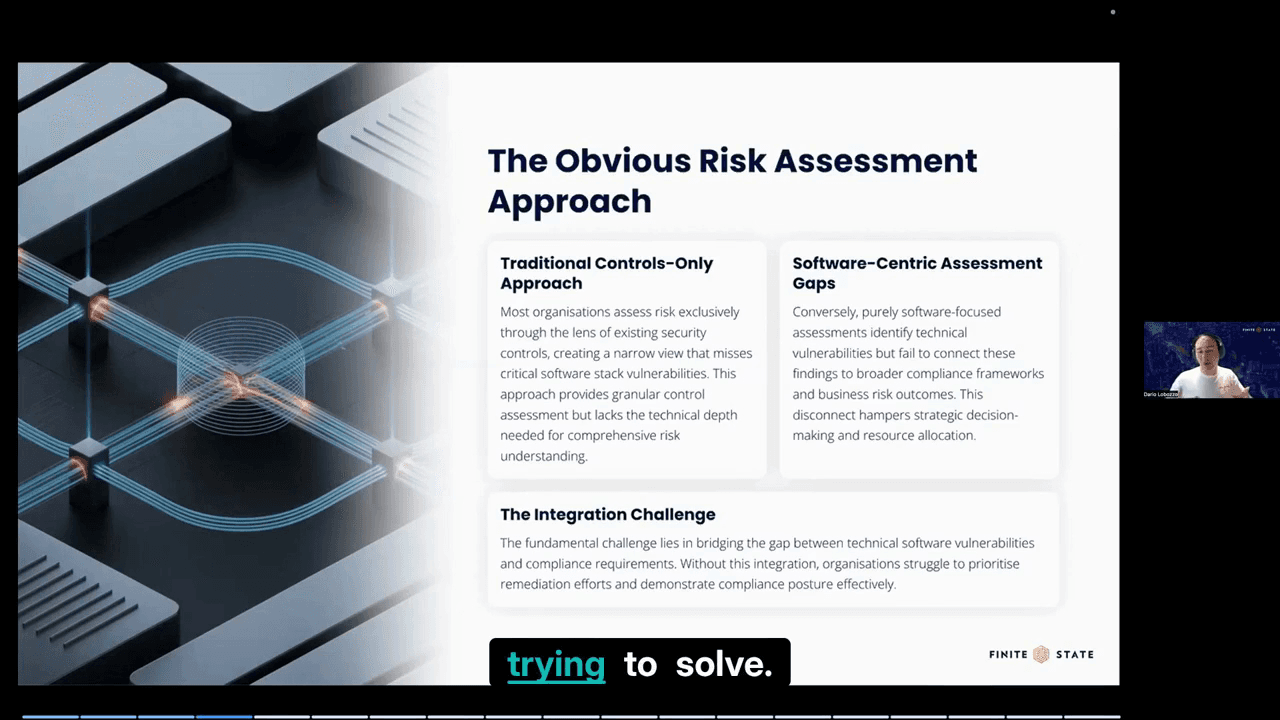
Where it doesn't work, though, is when you have a bigger team because, ultimately, what ends up happening is your fragmentation creates this complexity, and this gap of kind of going from the bottom up or the top down gets intensified as you start to have difficulty prioritizing which remediations are high risk, which remediations are high compliance risk, which may be different than human safety risk, which remediations are actually, if I apply it once, are going to have a broad level applicability.
How do those decisions and inefficiencies in those decisions impact the allocation of my security resources? Am I going to actually have enough security resources to accomplish all the various goals that I have set out for myself? All of these challenges are kind of inherent in this approach that is quite typical.