Hardwear.io 2026
Meet Finite State at Hardwear.io to explore how firmware analysis, exploitability-based vulnerability prioritization, and software supply chain visibility help security teams uncover hidden risks and secure connected devices.
Know What You Ship. Meet Finite State at Hardwear.io 2026
Connected devices introduce complex security challenges across firmware, embedded software, and third-party components. For security researchers, embedded engineers, and product security teams, the challenge goes beyond identifying vulnerabilities. It's understanding what's actually present in shipped firmware, determining which vulnerabilities represent real exposure, and managing risk across complex device ecosystems.
Meet Finite State at Hardwear.io 2026 to explore how deep firmware and binary analysis, reachability-driven vulnerability prioritization, and software supply chain intelligence help teams uncover hidden risks and focus on the vulnerabilities that matter most.
Go beyond vulnerability discovery. Understand real exposure.
Finite State is the Product Security OS for connected devices. We bring firmware and binary analysis, source intelligence, SBOM management, and exploitability-based vulnerability prioritization into one platform, helping security teams make defensible decisions grounded in what actually ships.
With Finite State, product security teams can:
- Uncover hidden firmware risks: Analyze firmware, binaries, and source code to identify vulnerabilities and components that traditional source-only tools may miss.
- Prioritize real exposure: Use reachability analysis and exploit context to distinguish actionable security risks from vulnerability noise.
- Gain software supply chain visibility: Build firmware-derived SBOMs, consolidate supplier data, and track third-party components across products and releases.
- Accelerate vulnerability response: Identify impacted products and builds, streamline triage, and support defensible vulnerability decisions with VEX workflows.
- Secure connected devices at scale: Maintain consistent security visibility and vulnerability intelligence across IoT, automotive, industrial, and consumer electronics ecosystems.
Join Roland Lindsey for a 90-minute technical session
Don't Trust the Robot: Judging AI-Found Vulnerabilities
Featuring Roland Lindsey, Chief Product Security Engineer, Finite State
When AI flags a critical vulnerability, how do you know if it's actually exploitable or just another false positive?
Join Roland Lindsey at Hardwear.io for an interactive, hands-on workshop exploring how to separate credible AI-generated vulnerability findings from false positives.
After six months of LLM-driven firmware teardowns across embedded Linux, industrial, automotive, and RTOS devices, the research identified 802 remote-code-execution findings, but only 68 were proven through reproducible exploits against shipped binaries.
In this 90-minute workshop, you'll step into the judge's seat and evaluate real, sanitized research findings across three interactive rounds:
- Would you ship this? Evaluate an AI-generated vulnerability finding and decide whether it's credible enough to report.
- Can you refute it? Challenge a plausible vulnerability claim and identify what the AI may have missed.
- Is this proof? Examine real exploit evidence and distinguish potential vulnerabilities from proven exploits.
Attendees will leave with a practical, reusable checklist for evaluating AI-generated security findings, applicable to firmware and beyond.
No firmware reverse-engineering experience, laptops, or special tools required.
Session Details
- Date: Thursday, November 19, 2026
- Time: 1:30–3:00 PM
- Location: Amsterdam Marriott Hotel
- Format: 90-minute interactive technical workshop
Let's talk at Hardwear.io
If your team is working to uncover vulnerabilities in firmware, assess real exploitability, strengthen software supply chain security, or improve vulnerability response across connected products, meet with Finite State at Hardwear.io.
We'll show you how Finite State helps security teams gain visibility into shipped software, prioritize real exposure, and make evidence-backed security decisions across every release.
Speakers
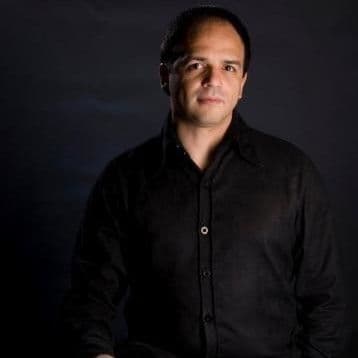
Roland Lindsey
Chief Product Security Engineer
Finite State