Our Capabilities
Secure
Secure Everything, Automated Threat Modeling
What it does
Drag-and-drop PDFs and architecture diagrams → structured STRIDE threat model in minutes
How it's grounded
Validates model against shipped binary—checks if vulnerable component actually exists
Why it matters
Threat modeling becomes maintainable, portfolio-scale workflow
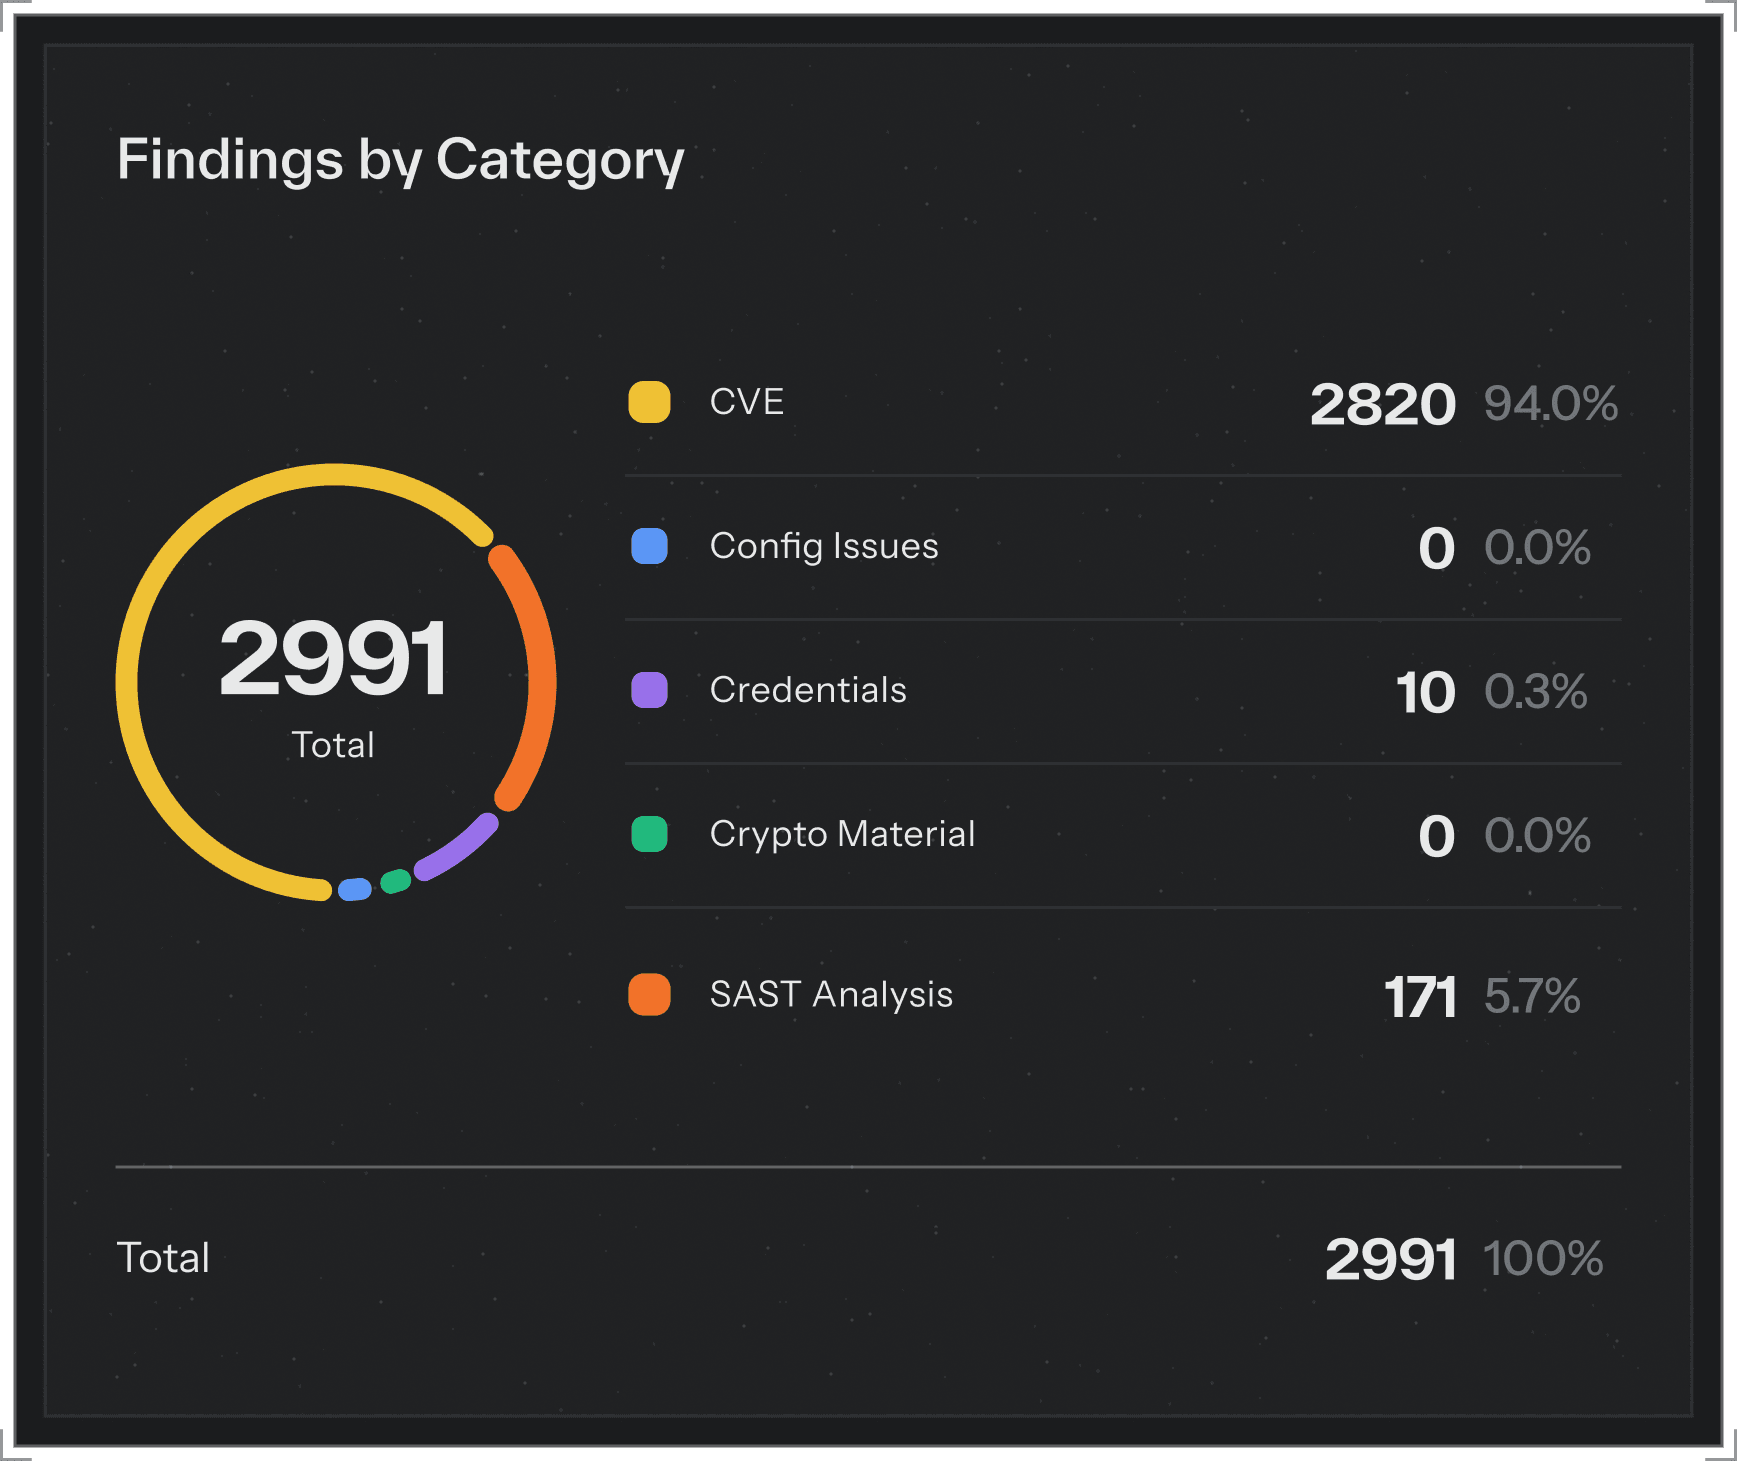
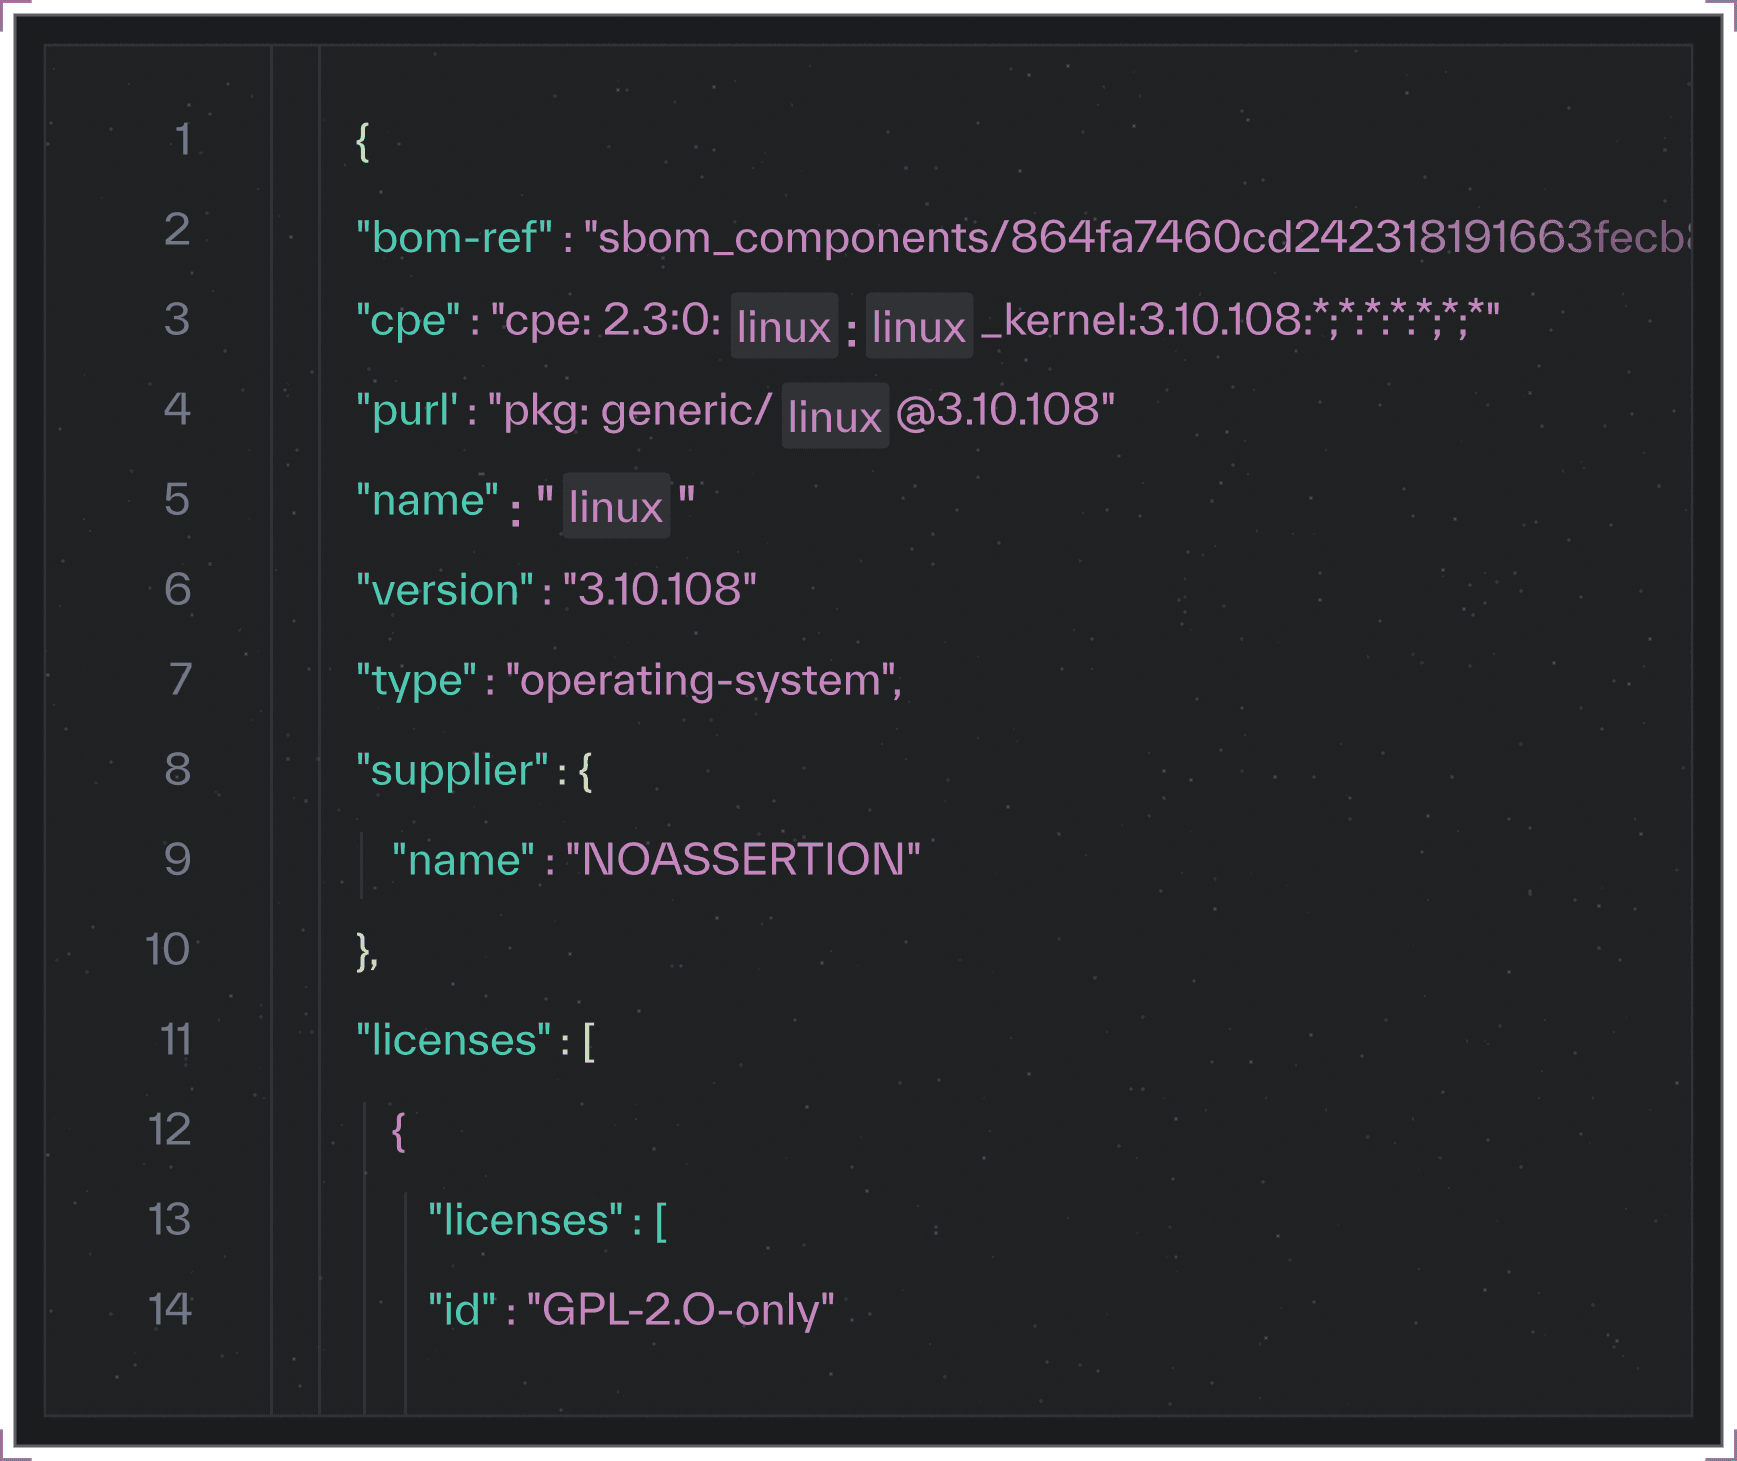
Scan
Scan Anything, Binary-Derived Ground Truth
What it does
Generate high-fidelity SBOMs reflecting what's actually inside your product
How it's grounded
Deep binary analysis identifies transitive dependencies source scanners miss
Why it matters
Security posture based on reality of software you ship
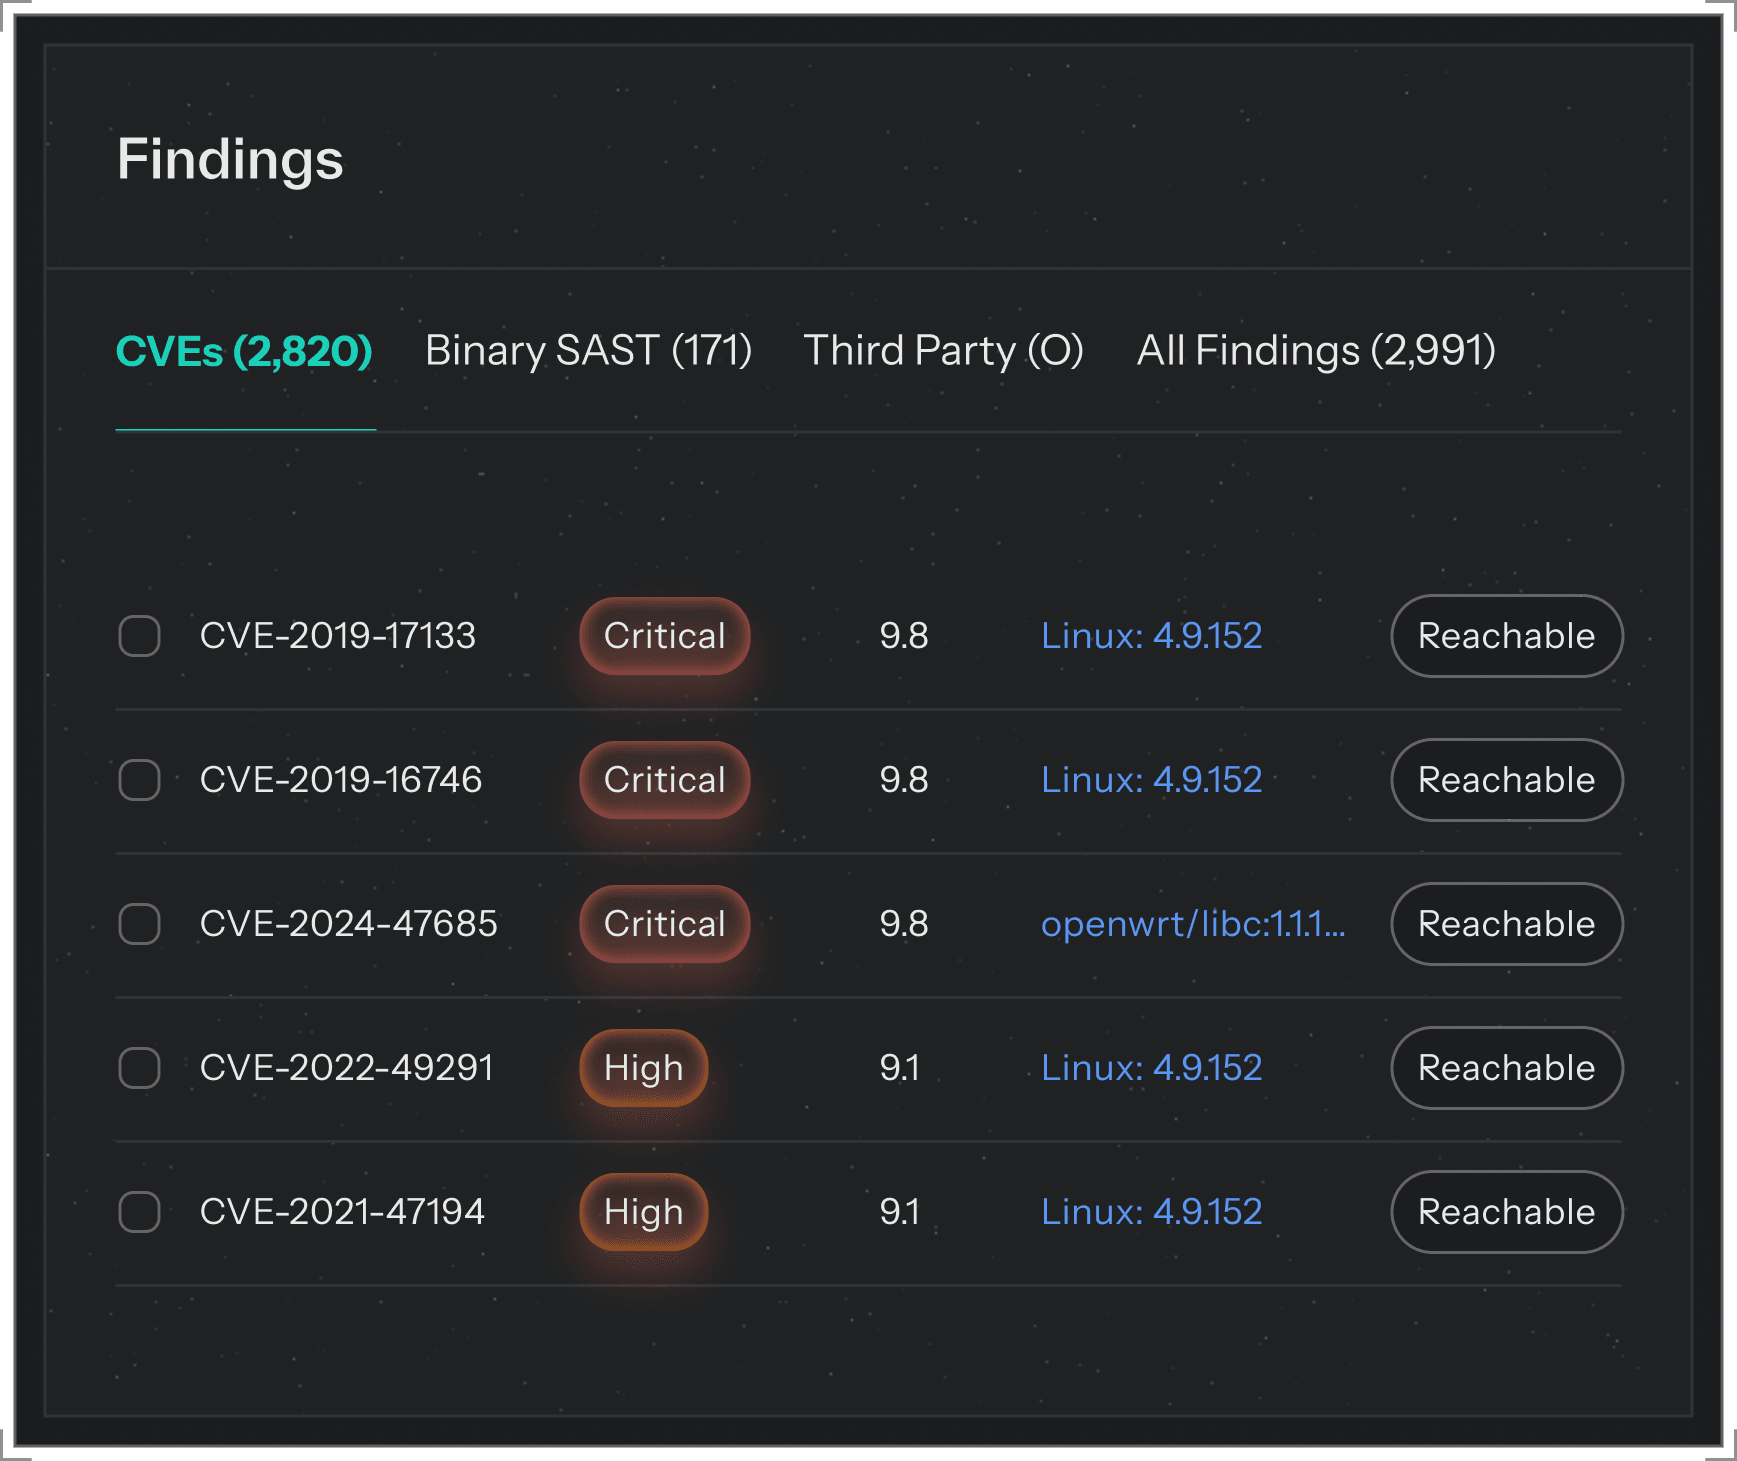
Fix
Fix What Matters, Verified Prioritization
What it does
Prioritize using real-hit risk analysis and exploit intelligence
How it's grounded
ISO 18045 aligned deterministic algorithms—audit-reproducible scores
Why it matters
Focus on issues that drive real exposure, reduce wasted cycles
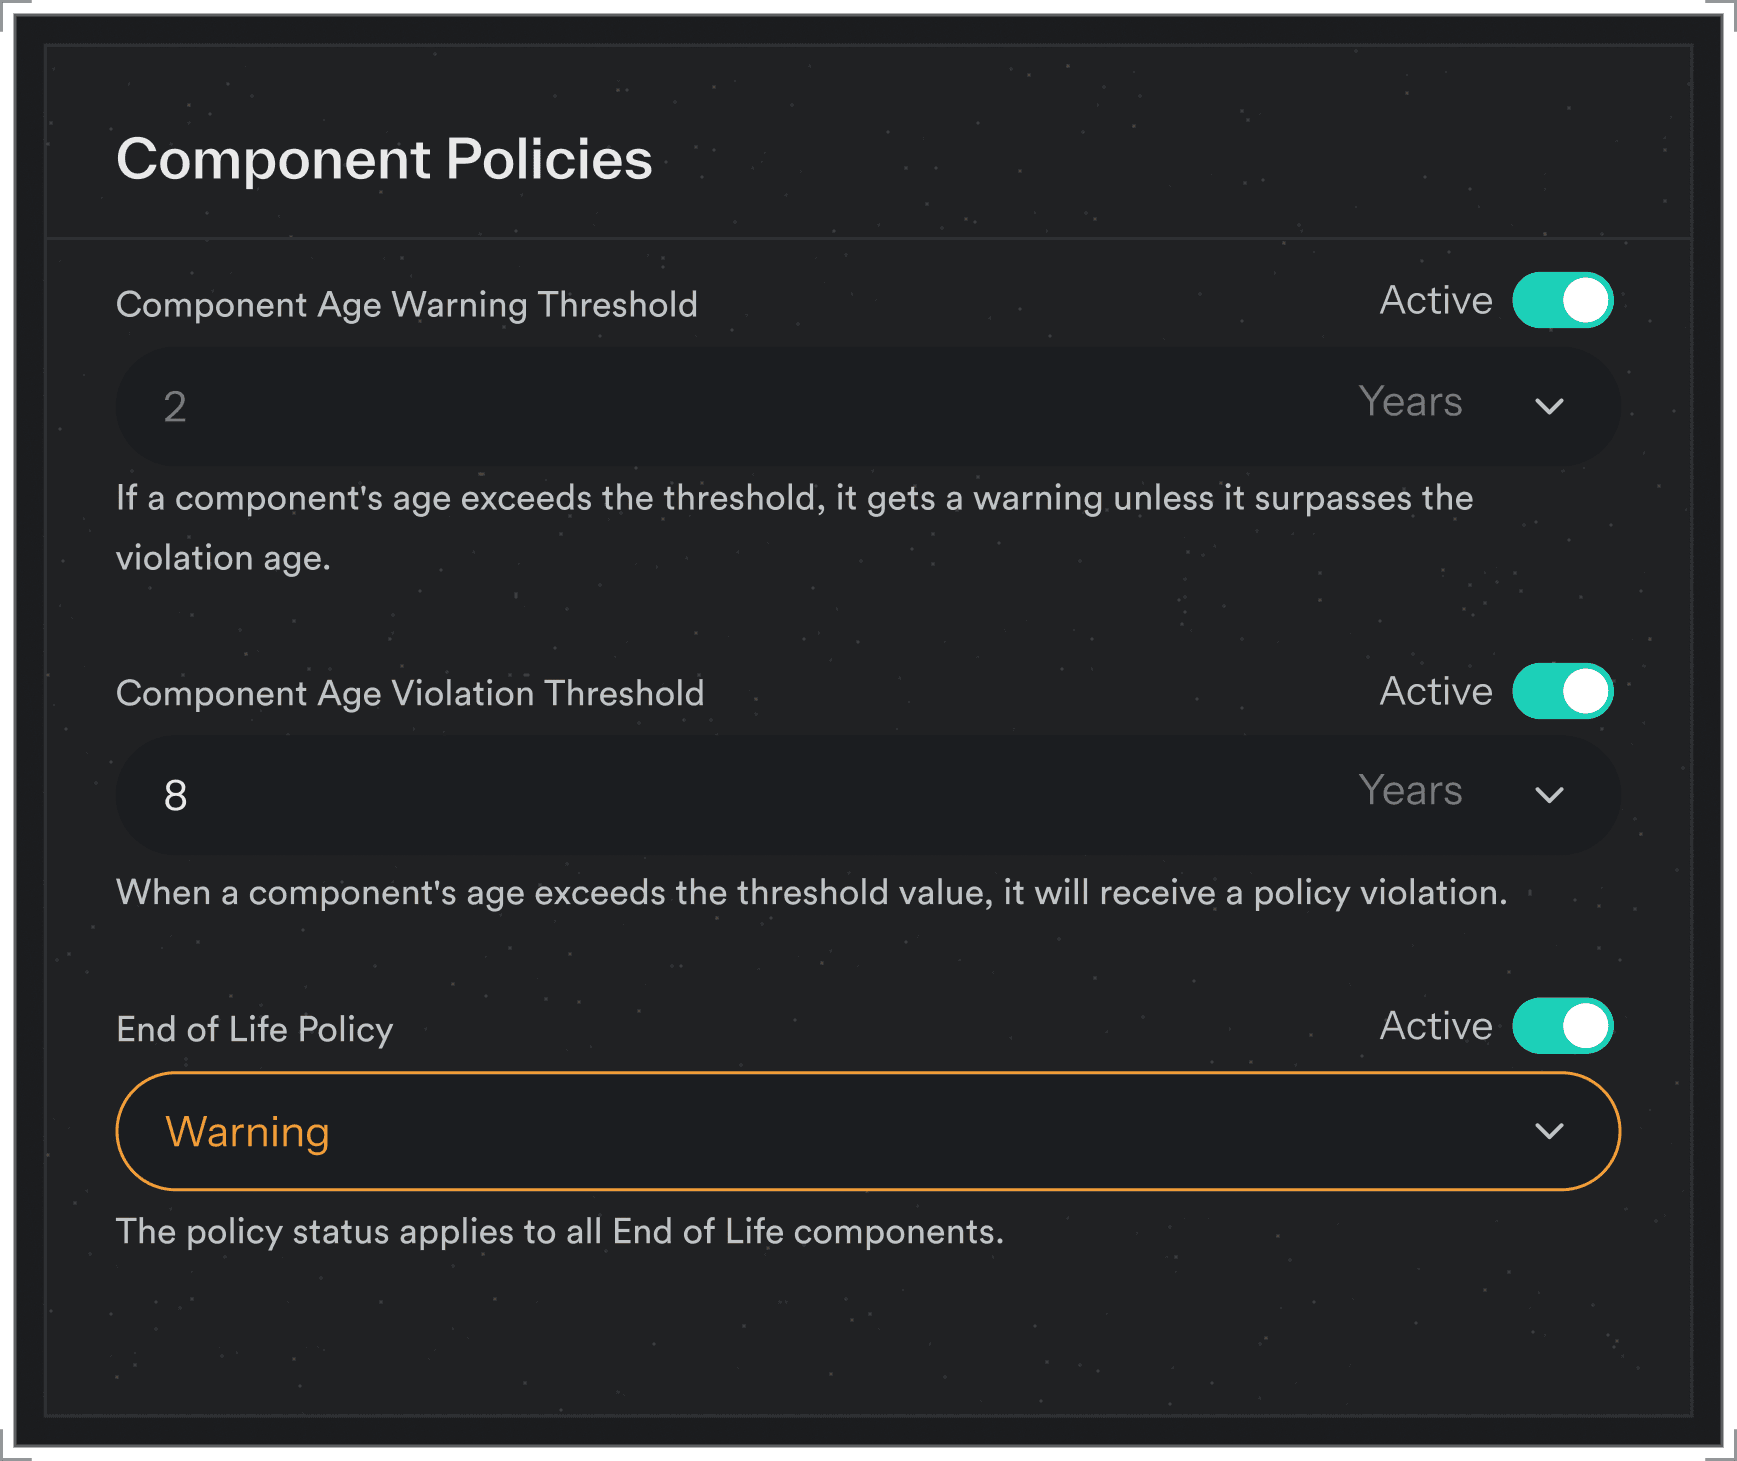
Certify
Certify Everything, Audit-Ready Compliance
What it does
One-click regulator-ready packages (EU CRA, FDA eSTAR, ETSI EN 303 645)
How it's grounded
Links every requirement to the threat it mitigates and binary evidence that proves the fix
Why it matters
Complete chain of custody for regulators upon release